> ## Documentation Index
> Fetch the complete documentation index at: https://docs.replit.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Advanced settings
> Set account-wide policies, add Workspace exceptions, and delegate supported settings to Workspace admins. Manage account seats, API access, and access requests.
Set consistent policies across your account without making every Workspace use identical settings. As an account admin, you can keep shared requirements central, add Workspace exceptions, and delegate supported settings to Workspace admins.
Use **Settings → Advanced** for account policies. Workspace admins manage delegated controls in **Workspace settings**. This page also covers account seats, the Admin API, and access requests.
Available settings depend on your role. Review [account and Workspace admin permissions](/teams/identity-and-access-management/account-and-workspace-admins) before changing policies.
## Account policies and Workspace controls
Choose how to manage each supported setting:
| Approach | Who manages it | When to use it |
| - | - | - |
| Account-wide policy | Account admin | Keep a shared requirement consistent across Workspaces. |
| Workspace exception | Account admin | Give a specific Workspace a different setting without changing the account-wide rule. |
| **Workspace managed** | Workspace admin, after the account admin delegates control | Let Workspace admins choose the setting for their teams. |
Delegation applies to individual supported settings, not every control. Workspace admins cannot change settings marked **Set by account policy**.
Screenshots show example values, not recommended defaults. Review each setting against your organization's requirements.
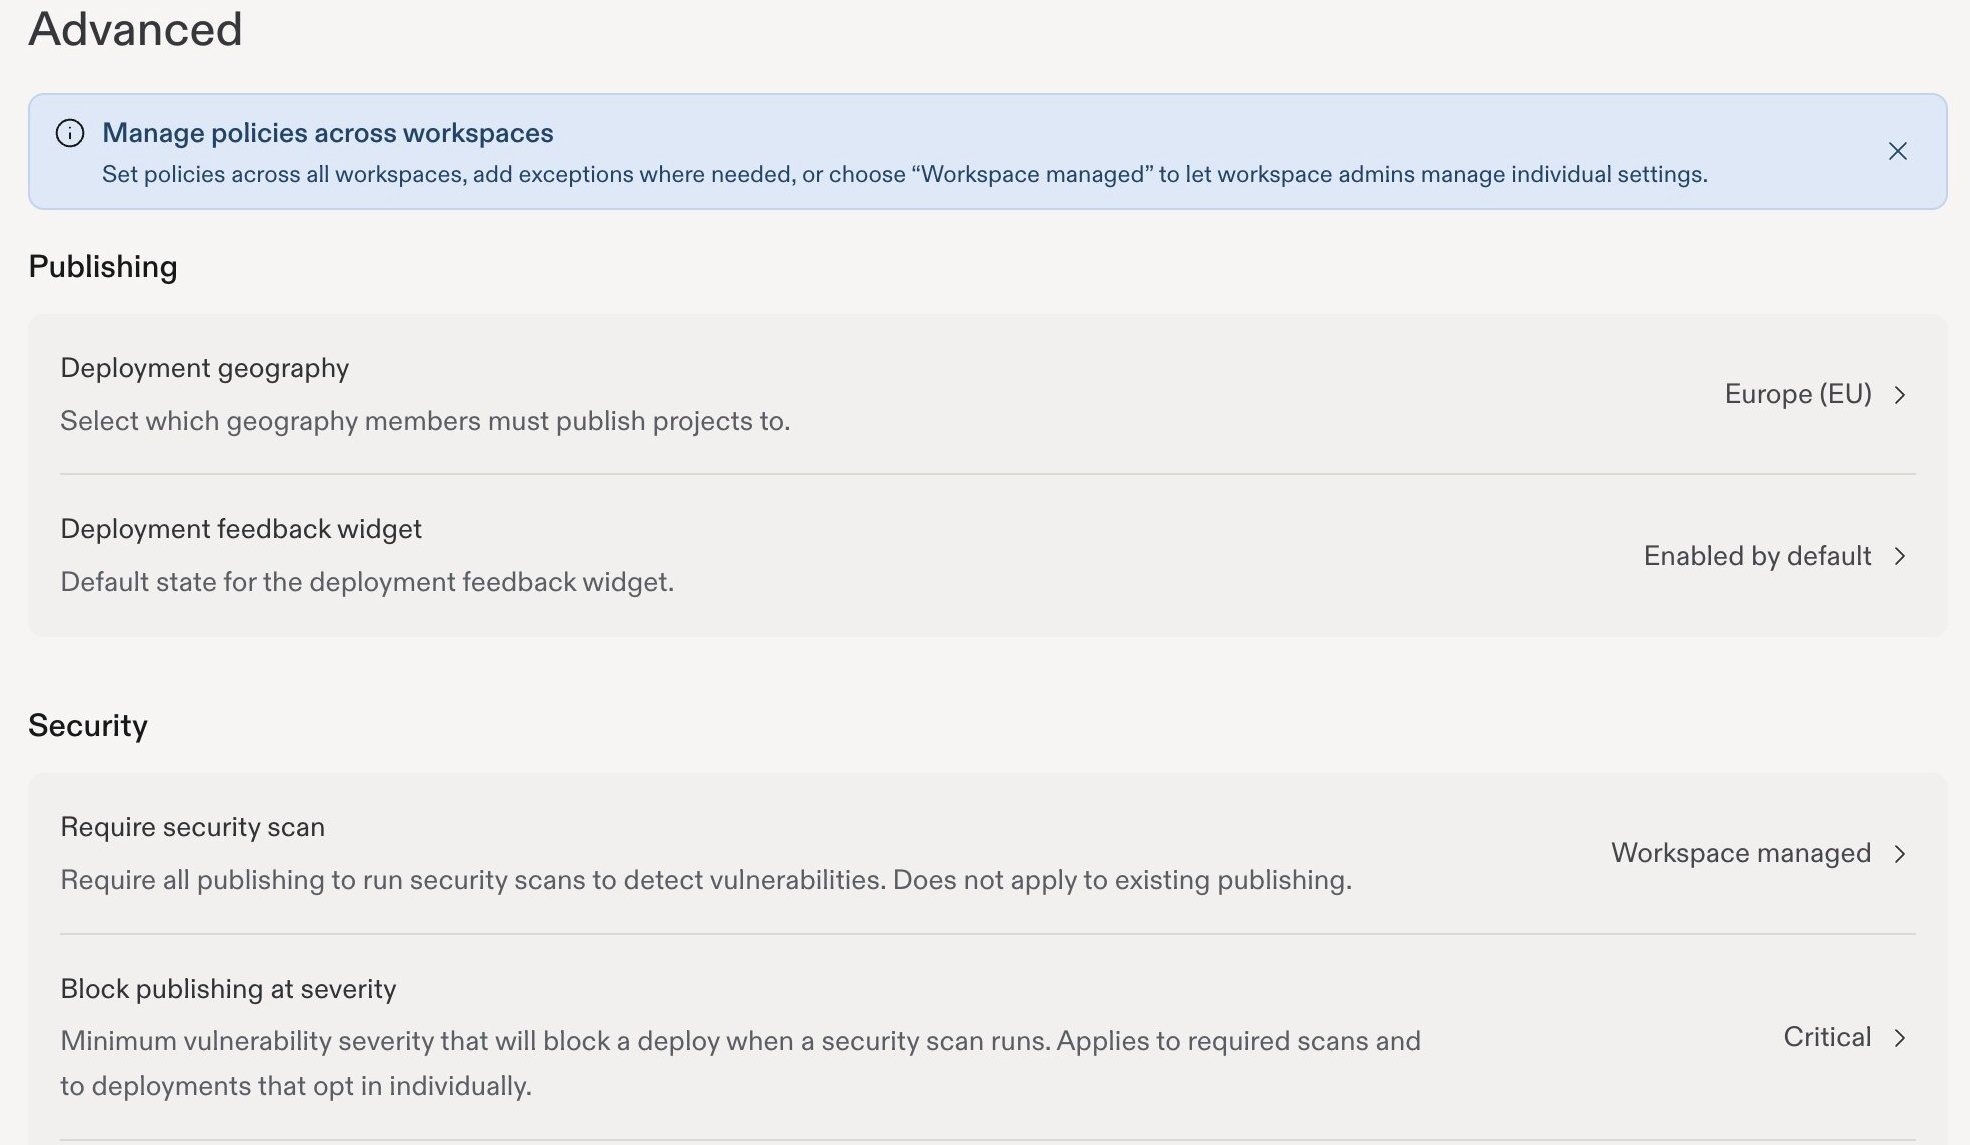
### Set account-wide policies
Account-wide policies let you manage shared requirements without configuring each Workspace separately.
1. Open **Settings → Advanced** in the **Account** section.
2. Select the setting you want to manage.
3. Choose the account-level value under **Account setting**.
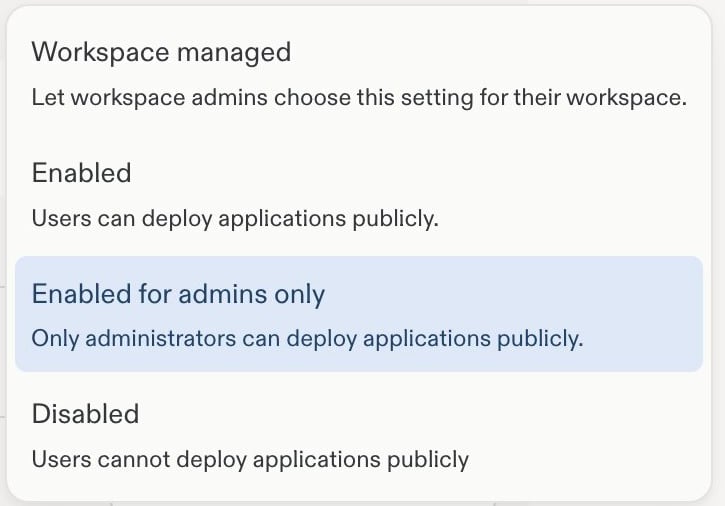
For example, **Public deployments** controls whether builders can publish apps publicly. **Enabled for admins only** limits public publishing to administrators.
 ### Add a Workspace exception
Use an exception when a Workspace needs a different rule. For example, you might restrict public publishing account-wide while allowing it in a Workspace for public-facing apps. To allow public publishing for a single project instead, use [public publishing exceptions](/teams/privacy-and-deployment-settings#public-publishing-exceptions).
1. Open the setting in **Settings → Advanced**.
2. Find the Workspace in the **Workspace settings** list.
3. Choose the value for that Workspace.
Account admins manage these exceptions. An exception differs from delegation: you choose the Workspace's value rather than letting its admins choose.
### Delegate a supported setting
Choose **Workspace managed** when Workspace admins should decide a setting for their own teams.
1. Open the setting in **Settings → Advanced**.
2. Open the account-level dropdown under **Account setting**.
3. Select **Workspace managed**, when available.
Workspace admins can then manage the delegated setting in **Workspace settings**.
 ### Manage delegated Workspace settings
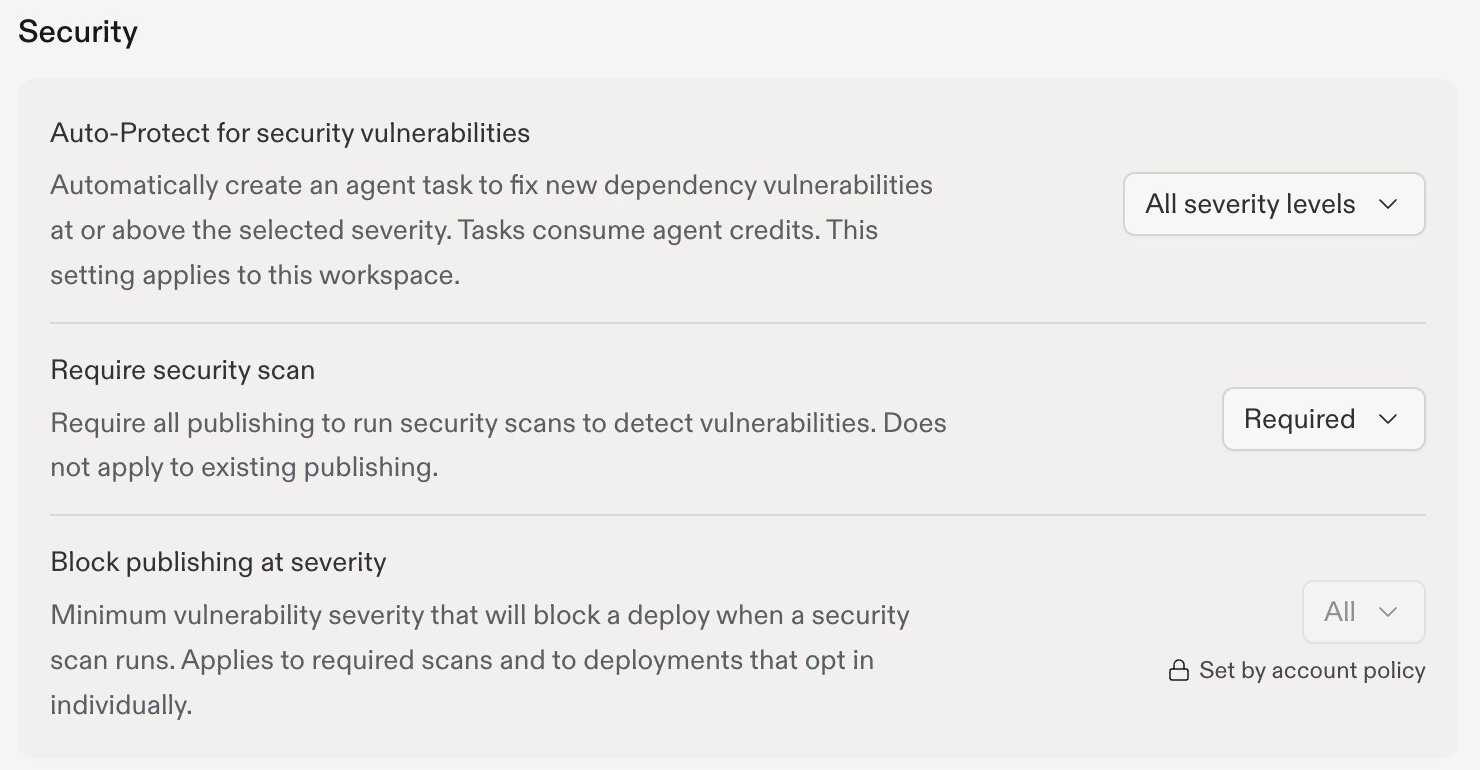
As a Workspace admin, open **Settings → Workspace settings** for your Workspace. Change the supported controls that your account admin has delegated.
Controls labeled **Set by account policy** are locked at the Workspace level. Ask an account admin to change the policy or configure an exception.
 ## Account seats
Open **Settings → Account seats** to review subscription seats across all your Workspaces. The page separates **Collaborators** and **Viewers**, showing used seats against the available allocation.
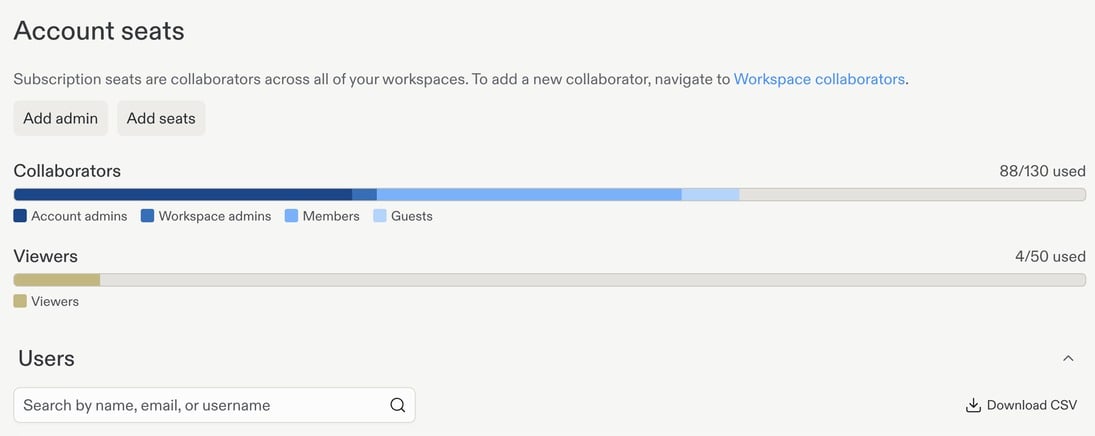 Use **Add seats** when your account needs more capacity, or **Add admin** to manage administrator access. The user directory below the totals lets you search by name, email, or username, review roles and last-active information, and **Download CSV**.
To invite a new collaborator, go to **Workspace collaborators** rather than the account-seat directory. See [Add collaborators](/teams/add-collaborators) and [account and Workspace admin roles](/teams/identity-and-access-management/account-and-workspace-admins).
## Admin API
The **Admin API** gives Enterprise account admins programmatic access to account information and supported administrative actions. Use it for internal reporting, usage dashboards, or operational integrations.
Open **Settings → Developer → API keys** and select **Create API key** to get started.
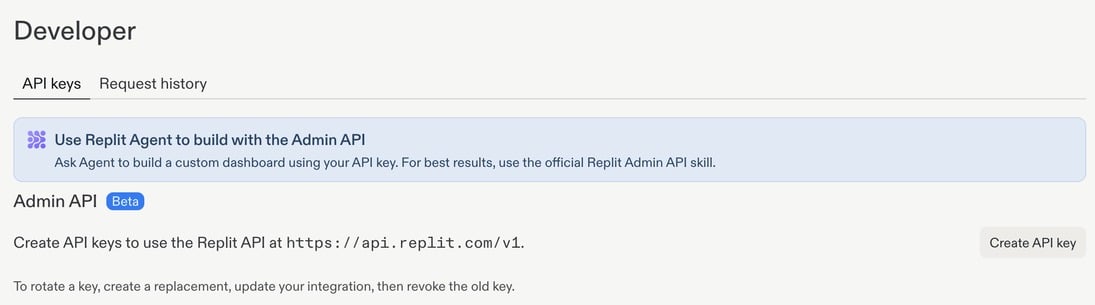 For example, use the API to build a dashboard that compares usage across Workspaces. See the [Admin API guide](/teams/admin-api) for access requirements, scopes, and setup.
The Admin API is in beta and is available only to Enterprise account admins. Grant each key only the access it needs and store it in a secure secret manager. Never put API keys in documentation, screenshots, or chat.
## Access requests
Open **Settings → Advanced → Access requests** to choose which requests are available in each Workspace. These controls let people ask for additional access when they reach a limit or encounter a policy restriction; making a request available does not automatically grant it.
Review these requests with the [Admin API](/teams/admin-api#what-you-can-do), which can retrieve, approve, or deny them. Settings does not include an approval inbox.
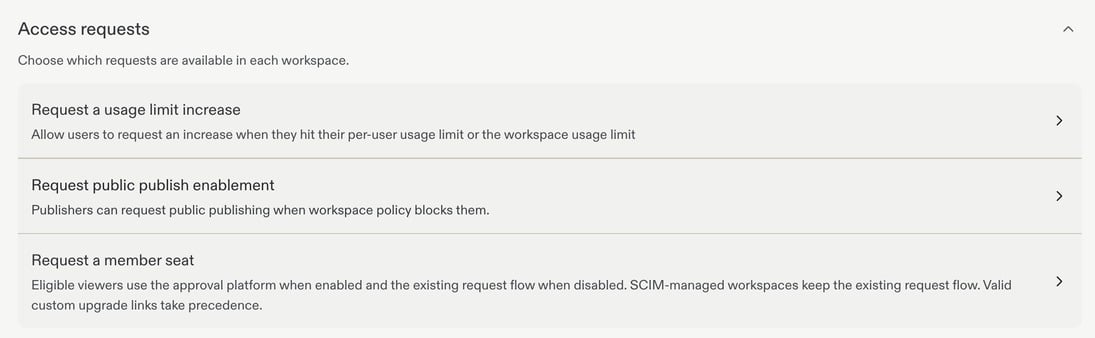 | Request | Purpose |
| - | - |
| Request a usage limit increase | Let builders request an increase when they reach their per-user or Workspace usage limit. |
| Request public publish enablement | Let publishers request public publishing when Workspace policy blocks it. |
| Request a member seat | Provide an approval route for eligible viewers who need a member seat. |
Select a request type to review its Workspace settings. For example, **Request a usage limit increase** offers an **Enabled** or **Disabled** setting for each Workspace.
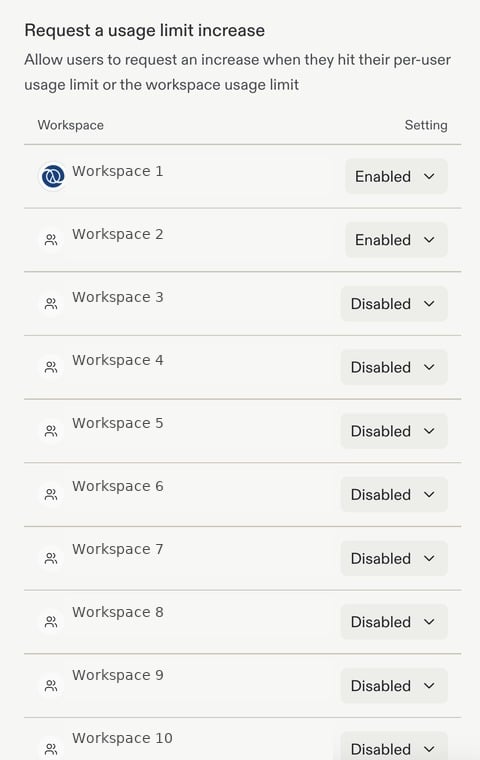 Member-seat requests have additional routing rules: SCIM-managed Workspaces keep their existing request flow, and valid custom upgrade links take precedence.
## Other administrative controls
* [Privacy and deployment settings](/teams/privacy-and-deployment-settings): Control publishing privacy and deployment geography.
* [Model controls](/teams/modes-and-model-providers): Choose approved models and effort options.
* [Observability](/teams/observability): Review consumption and audit logs.
* [Standardization](/teams/standardization): Share reusable workflows and design guidance.